
SSO Domain Restrictions
This feature is only available in the OpenObserve Enterprise Edition.
This user guide provides step-by-step instructions for configuring and managing SSO Domain Restrictions in OpenObserve.
This feature allows you to control which users can log in to OpenObserve using Single Sign-On (SSO) providers. You can allow or block specific domains or individual users from those domains.
Where to find
The page is available in the _meta org under Settings > SSO Management (under Access & Security). The restrictions are in its Domain Restrictions section.
Who can access
Root user and any other user who has access to the _meta org can access the SSO Management page.
Add Domain Restrictions
Step 1: Add a new domain
Step 1: Add a new domain
- In the Domain and allowed users section, enter the domain name in the text field.
Enter only the domain name, for example,
example.comand do not include the@symbol.
- Click the Add Domain button.
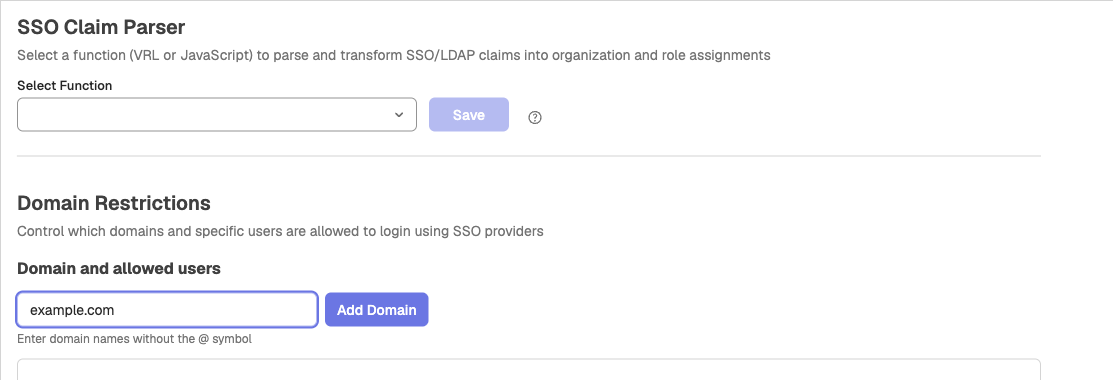
Step 2: Configure Domain Access
For each domain, you have four control options:
Option 1: Allow All Users from Domain
It permits any user with an email address from the selected domain to log in using SSO.
Use case: Allow all employees from your company domain
@example.com.
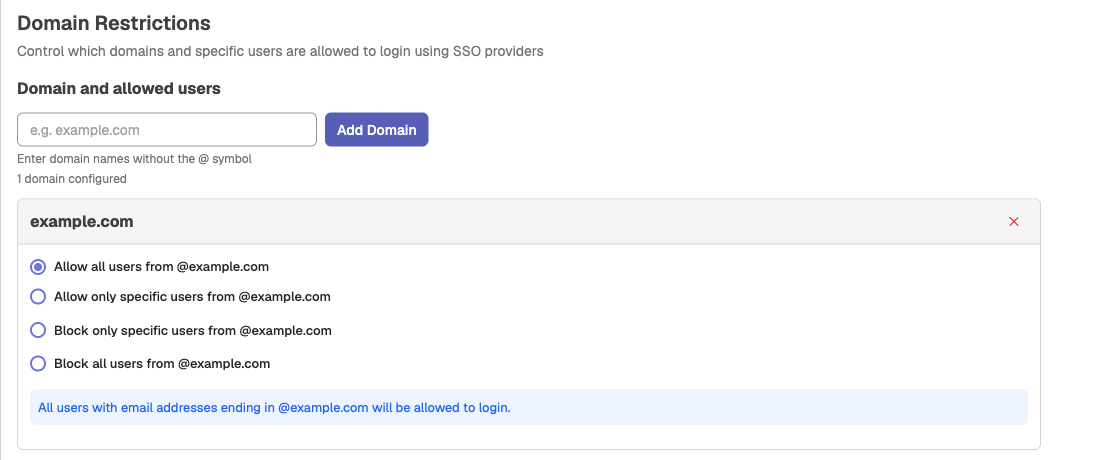
Option 2: Allow Specific Users Only
It allows you to add individual email addresses that should be permitted to log in using SSO.
Use case: Allow only certain users from a partner organization. For example,
e1@example1.comande2@example1.com.
When Allow only specific users is selected:
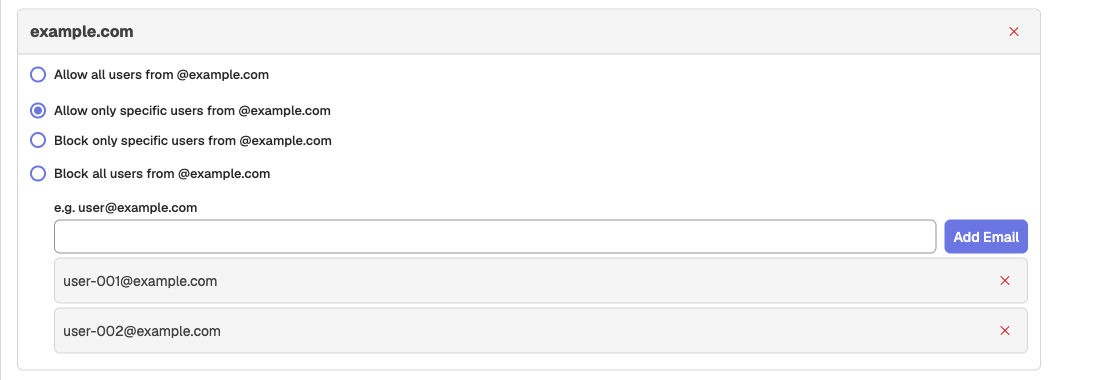
- Enter the complete email address in the input field.
- Click Add Email.
- The email address will be added to the allowed list.
- Repeat for additional users.
- Use the X button next to any email to remove it.
Option 3: Block All Users from Domain
All external SSO users with email addresses from the domain are blocked from the system, including the UI, API and ingestion.
Option 4: Block Only Specific Users
Enter each email address to block and click Block Email.
Blocked entries apply to external SSO identities only (SSO users and SSO/token service accounts). They override any allow rule and cover the UI, API and ingestion. Native and API-created accounts are not affected; delete those instead.
Step 3: Save configuration
Step 3: Save configuration
- Review your domain restrictions.
- Click Save to apply the configuration.
- Click Cancel to discard changes.
SSO claim parser
The same page has an SSO Claim Parser section. Use Select Function to pick a function from the _meta org that parses SSO/LDAP claims (such as email, name, groups and roles, as mapped in Dex) into organization and role assignments. The section also lists Recent Errors (Last 24 Hours) from the function.
Domain limits
There is no limit on the number of domains you can configure. Add as many domains and specific users as needed for your organization.
Error messages
When SSO Domain Restrictions are configured, any user attempting to log in from domains or email addresses that are NOT in the allowed list will see an unauthorized error during SSO login.
Supported SSO login options
OpenObserve allows users to log in through the following Single Sign-On options, and domain restrictions apply to all of them:
- GitHub
- GitLab
- Microsoft
Domain restrictions will be enforced when users attempt to log in using any of these SSO options.
Troubleshooting
| Problem | Solution |
|---|---|
| SSO Management menu not visible. | Verify that you are in the _meta organization. |
| Changes not taking effect. | Ensure that you clicked Save and refresh the login page. |
Nodes in OpenObserve
Monitor node health and performance in OpenObserve clusters, including CPU, memory, and TCP connections across ingesters, queriers, and other node types.
Domain to Organization Mappings
Map email domains to organizations in OpenObserve Cloud so users who sign in are added to the right organization with the correct role automatically.